The problems encountered
Device passwords that have to be handed to installation companies, authorisations that cannot be taken back afterwards, NVRs that can be discovered with a port scan, servers left outside the firewall, lines paralysed by a simple DDoS, branch cameras that can be disabled remotely, post-incident review being impossible because there is no central log, inventory that cannot be kept current, and use of the line outside its purpose going unnoticed. The common cause of all of these is that devices are managed one by one, from the local interface and with permanent passwords.
How OBIFI solves it
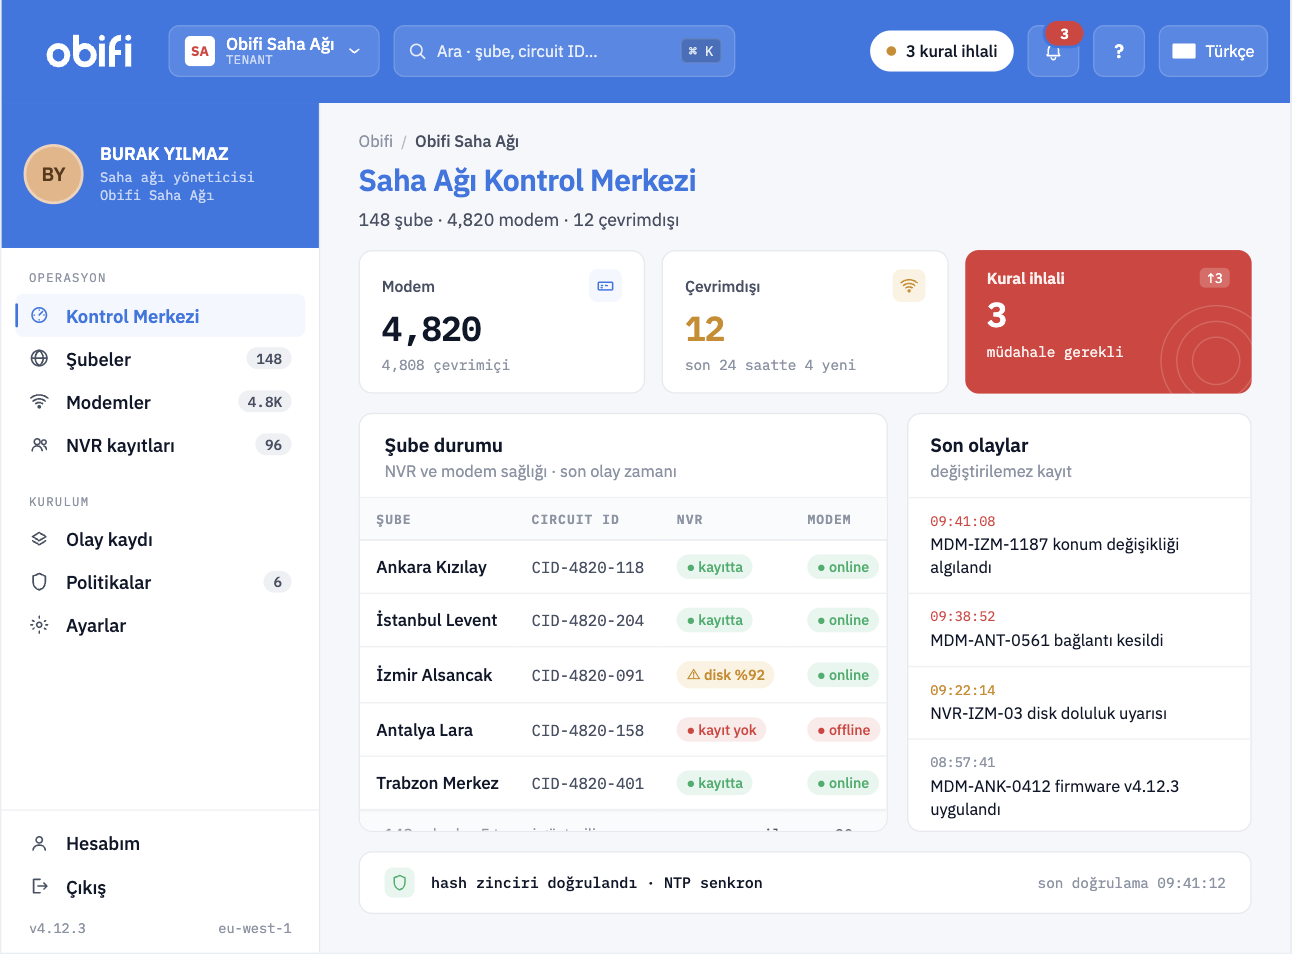
Management is brought to the centre; devices run OpenWrt-based OBIFI firmware, their interfaces are locked and no free access remains in the field. Default passwords are changed in bulk on day one. Installation, replacement and fault intervention run through an approval flow; the technician does the work with a temporary token. Every device is identified per circuit, port and VLAN with DHCP Option 82, and static IPs go away. Every modem reaches only the defined destinations; an alarm is raised the moment a rule is breached. All operations are collected in an immutable log and kept with an NTP timestamp and hash verification. Faults drop into the existing CRM automatically, and NVR/alarm emails are parsed and turned into events. Physical movement of a modem is caught with base station data.
Deployment model
It is installed on-premise, in an environment closed to the internet, with active-active HA. Pilot verification is carried out at agreed branches before acceptance. Administrator and end-user training and installation and usage manuals are part of the delivery. A maintenance service with 24/7 call acceptance and a defined response time is offered for critical software-related faults; patch processes and remediation times for vulnerability reports are given in writing in the contract.
Who it is for
Public institutions with a widespread branch network, banks and retail chains, security operations centres, alarm monitoring centres, and critical infrastructure operators.